FEATURES

Video Interviews

Most Container Images You Pull Today Are Already Full of Vulnerabilities

Most Container Images You Pull Today Are Already Full of Vulnerabilities

|
Container image security has quietly stayed stuck on the same problem it had a decade ago. Finding vulnerabilities is trivial ...
Why Kubernetes Utilization Is Stuck Below 40%

Why Kubernetes Utilization Is Stuck Below 40%

|
Kubernetes was sold on the premise that clusters would scale themselves into efficient, elastic infrastructure. The reality on most production ...

LATEST FROM DEVOPS.COM

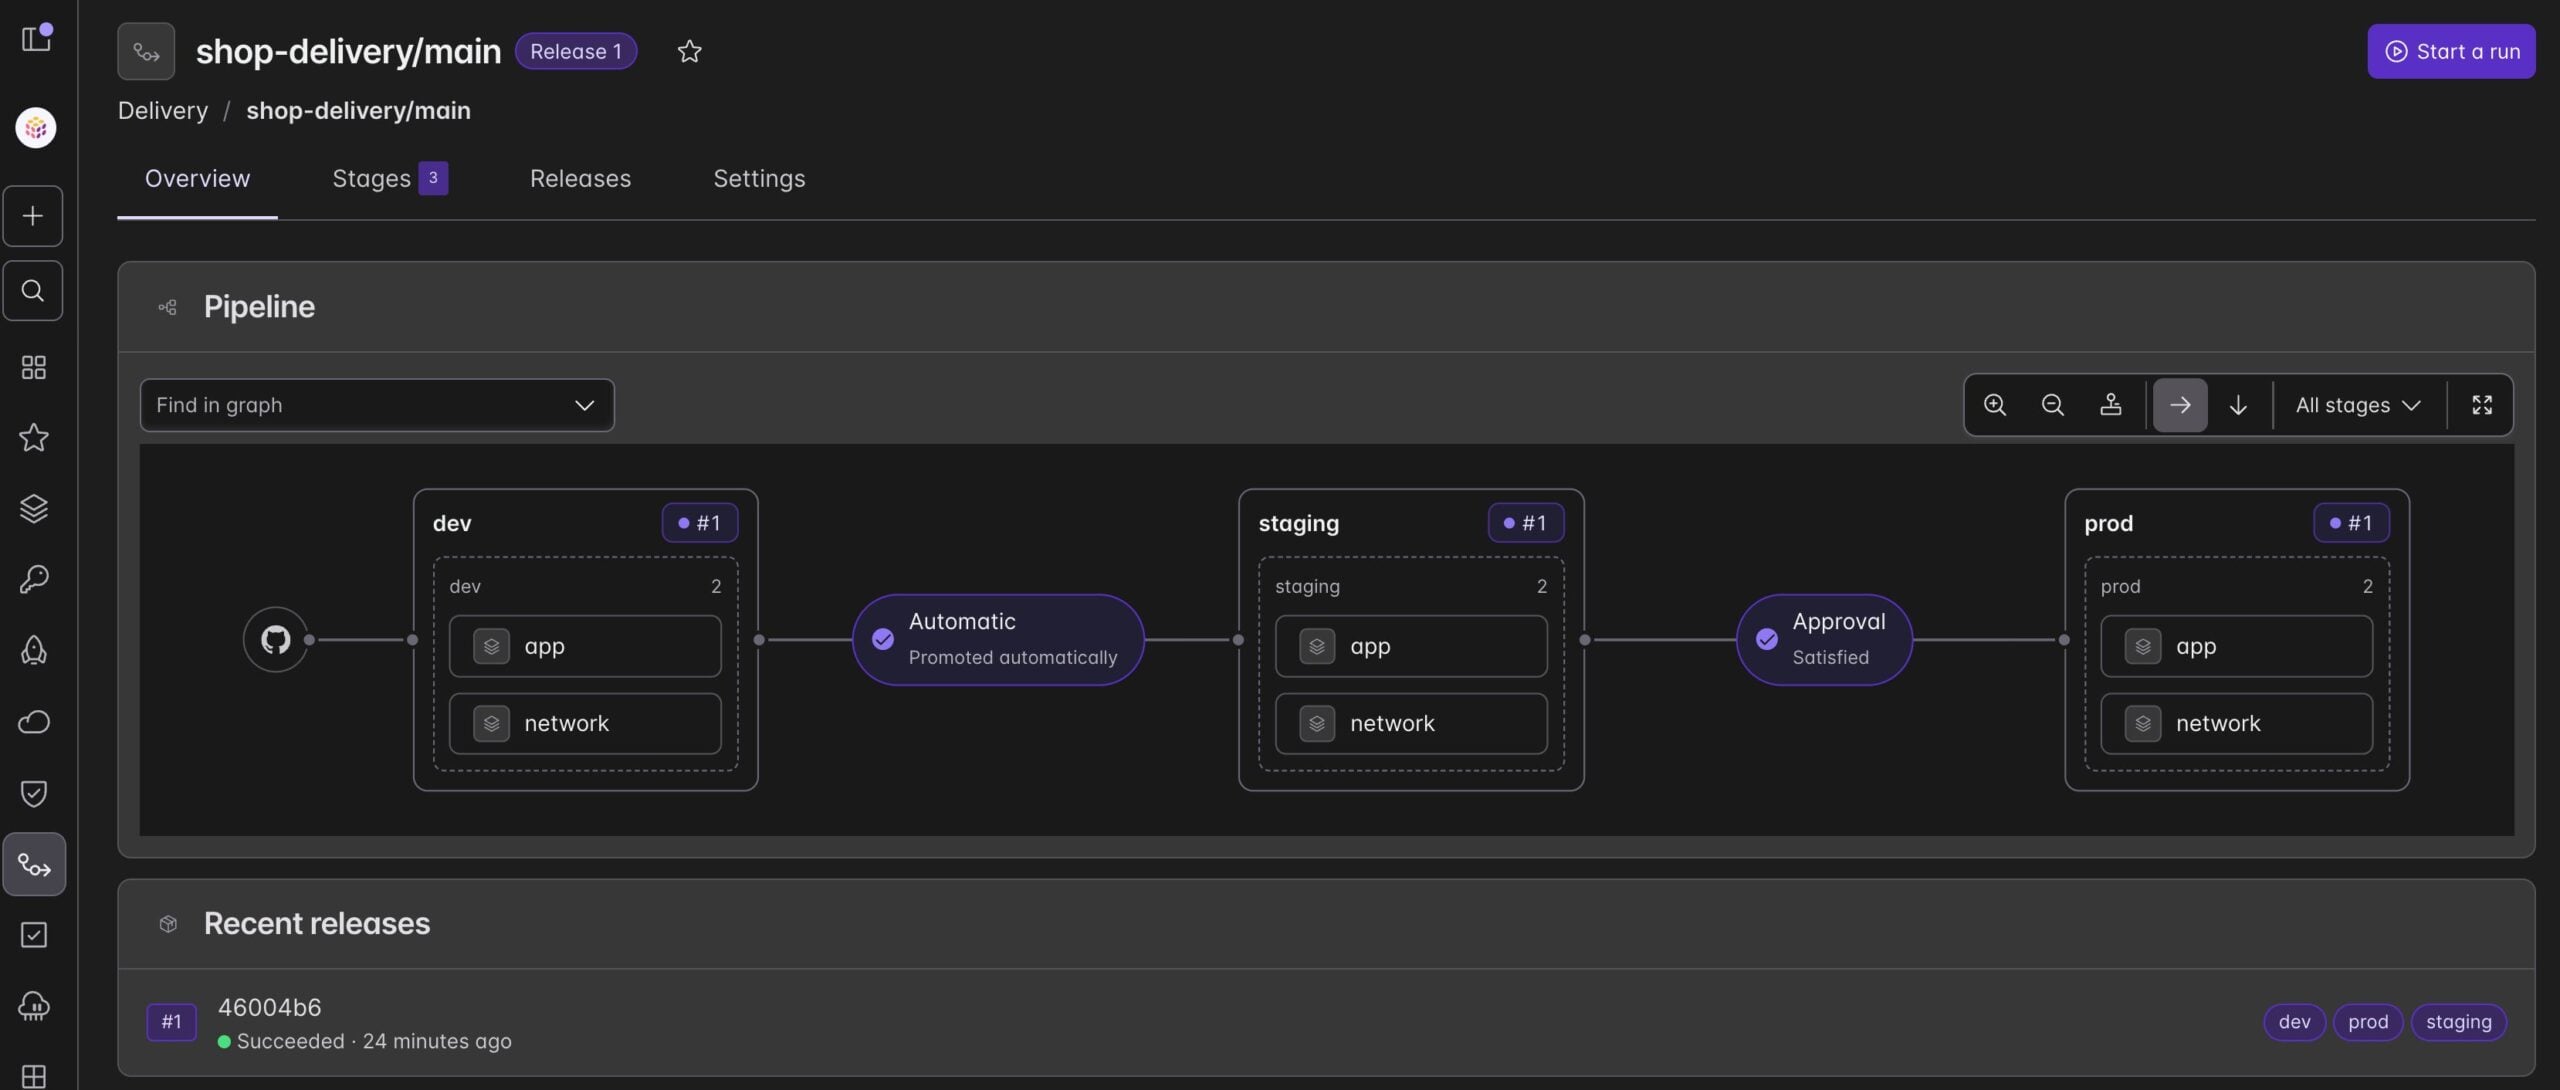
Pulumi Previews DevOps Platform Extensions for the Agentic AI Era

Pulumi today made available in public preview both an ability to enable DevOps teams to define delivery pipelines in code and a series of artificial intelligence (AI) agents that have been trained to perform specific tasks. A Pulumi Delivery capability makes it possible to use TypeScript, Python, Go, and other languages to create pipelines for […] [...]

The security firm behind last month’s high-profile PHP2Shell discovery has used AI to uncover another serious vulnerability, this time in Java. Calif says its researchers have demonstrated remote code execution in widely used Java applications, including Jenkins and JFrog Artifactory. The vulnerability, called Java4Shell and tracked as CVE-2026-114938, involves an out-of-bounds memory write in OpenJDK’s […] [...]

Chainguard has long been a leading software supply chain security company, and now it’s making it easier and cheaper to access its secure open-source software offerings. Back in 2022, Chainguard co-founder Kim Lewandowski said, “Chainguard’s mission is to make the software supply chain secure by default, because we think the only way you can get […] [...]